OnlyFans account security demands verification steps that generic password advice fails to address. BestOnlyFans analysis shows subscribers face distinct risks combining financial exposure, billing discretion concerns, and social engineering tactics that exploit platform stigma. This guide covers the specific vulnerabilities standard recommendations miss. BestOnlyFans refreshes its rankings every month.
Why OnlyFans Accounts Face Distinct Threat Profiles
OnlyFans subscribers encounter targeting patterns that differ from general consumer platforms. The combination of recurring billing, adult content association, and desire for discretion creates multiple exploitation angles that attackers actively develop.
Financial data concentration drives initial targeting. Subscription prices range from $4.99 to $49.99 monthly, though typical paid subscriptions cluster between $4.99 and $15, with averages around $5 to $10. Many users maintain multiple subscriptions, and some add pay-per-view purchases up to $50 per message or paid chat interactions at $3 to $5 per message. This recurring revenue stream makes account credentials valuable for both direct theft and resale.
Billing discretion desires create psychological leverage. Attackers understand that subscribers often prefer resolving issues privately rather than involving banks or family members who might see statements. This dynamic reduces reporting rates and extends the window for fraudulent activity.
Content sensitivity further suppresses incident reporting. Victims of account compromise hesitate to seek help through normal channels, fearing exposure of their subscription history. Platform structure compounds these factors—OnlyFans has no built-in discovery feed or directory, meaning users rely on external sources to find creators. This dependency creates opportunities for malicious intermediaries and fake profiles that capture credentials before legitimate subscription occurs.
Authentication Layers Beyond Password Complexity
Password length alone insufficiently protects OnlyFans accounts given the targeting patterns described above. Multi-factor authentication implementation requires specific configuration choices that many users overlook.

The authentication stack should include these elements:
- Unique 16+ character password stored in a password manager, never reused across services
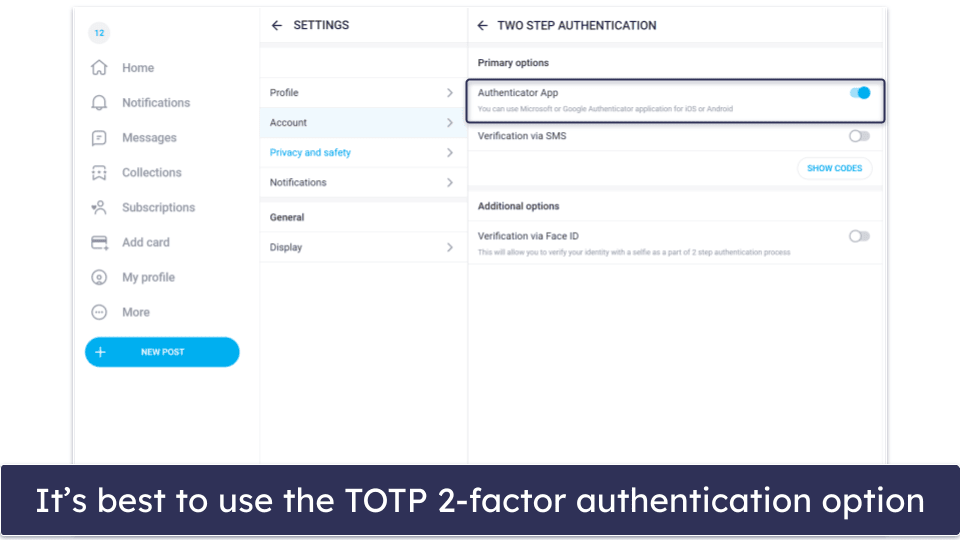
- Authenticator app preference over SMS-based codes due to SIM swap vulnerabilities
- Recognized device limits set to flag unfamiliar access attempts
- Login notification enablement for immediate awareness of account access
SMS interception presents a documented risk for high-value targets. Authenticator apps eliminate this vector. The platform supports standard TOTP implementation compatible with common applications.
Device management requires active attention—review active sessions quarterly and remove unrecognized devices immediately. Geographic anomalies in login locations demand immediate password changes. Free pages add complexity: creators who set their base price to $0 earn via tips and PPV messages, meaning subscribers to free accounts still face payment method exposure even without recurring charges. Financial compartmentalization limits exposure from any single breach. OnlyFans subscription management benefits from dedicated payment instruments that separate platform activity from daily spending.
Implement isolation through these steps:
Payment Method Isolation and Monitoring
- Establish dedicated virtual card or single-purpose physical card for platform use only
- Set credit limit below daily transaction cards to contain potential fraud scope
- Configure immediate transaction alerts for any charge above $0.50
- Cross-check monthly statements against actual active subscriptions
Payment approach comparison clarifies the isolation strategy:
| Card Type | OnlyFans Visibility | Recommended Use |
|---|---|---|
| Primary daily credit card | High visibility | Avoid for platform subscriptions |
| Dedicated low-limit card | Moderate visibility | Acceptable with monitoring |
| Virtual card service | Containerized visibility | Preferred approach |
| Prepaid debit | Limited functionality | Restrictive but safe option |
Virtual card services generate single-purpose numbers that limit merchant exposure. If credentials leak, the number cannot be used elsewhere.
Billing descriptor variation complicates monitoring. OnlyFans charges may appear under multiple merchant names. Document legitimate descriptors when subscriptions begin. The $0.10 verification hold during initial card addition refunds within days but indicates successful card testing. Note that while promotional first months can drop to $3, the base price minimum remains $4.99, and auto-renew stops if a creator later raises their price—though your existing access continues until the paid period ends.
Recognizing Phishing Tailored to OnlyFans Subscribers
Social engineering against OnlyFans users exploits platform-specific knowledge that generic phishing lacks. Attackers research billing cycles and subscriber concerns to craft convincing lures. BestOnlyFans methodology incorporates security incident patterns observed across ranking data to identify emerging threat types.
Common indicators of targeted phishing include:
- Urgency messaging around billing discretion or statement appearance
- Requests to verify identity outside onlyfans.com domains
- Creator direct messages containing external links or payment requests
- Refund promises requiring credential re-entry on unofficial sites
- Threats of subscription history exposure to contacts or employers
Threat vector mapping guides verification response:
| Threat Type | Delivery Method | Verification Response |
|---|---|---|
| Credential harvesting email | Link to fake login page | Check sender domain, never click links |
| Direct message urgency | Platform DM with external contact request | Verify through platform directly, ignore external paths |
| Phone call reference | Claimed support call | OnlyFans does not call subscribers |
Creator impersonation deserves particular attention. Popular accounts attract impersonators who message recent followers with promotional offers requiring off-platform payment. Legitimate creators conduct all transactions through platform systems exclusively.
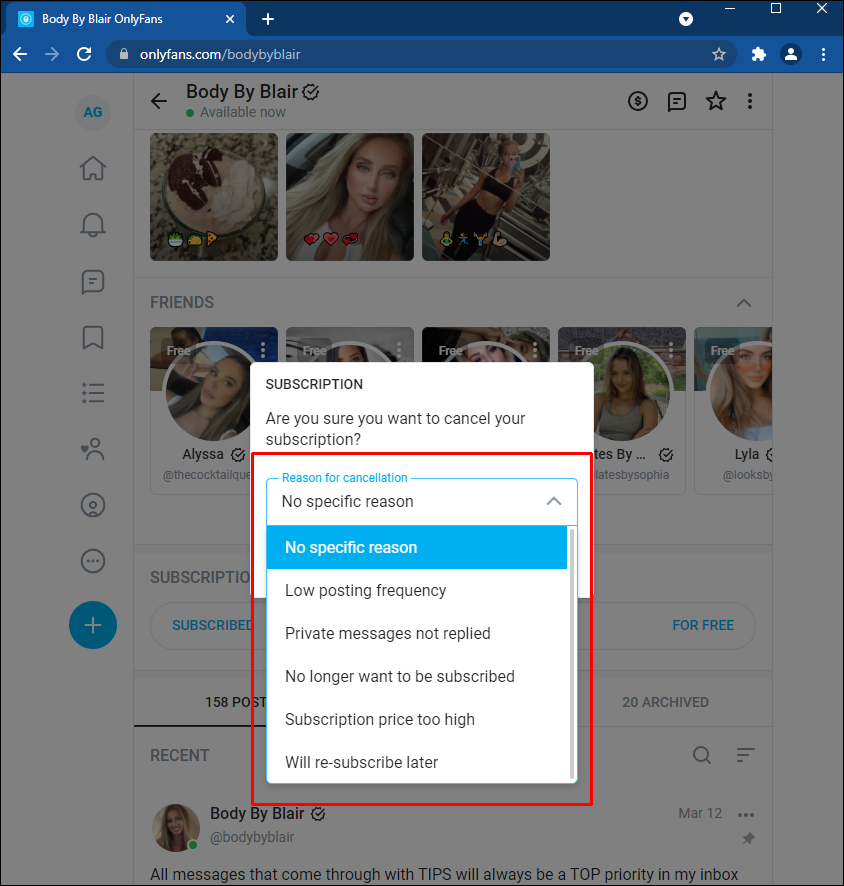
Fake refund operations exploit cancellation concerns. Subscribers seeking to cancel may encounter fraudulent sites that capture credentials under the guise of processing refunds. The cancel-subscription dialog provides legitimate cancellation paths without credential re-entry.
Account Recovery Preparation Before You Need It
Recovery access often determines whether compromise becomes temporary inconvenience or permanent account loss. Preparation steps completed during normal access prevent cascade failures.
Verified email maintenance is critical. Recovery emails must remain accessible. Abandoned addresses that once registered the account create permanent recovery barriers.
Backup payment methods provide alternative verification paths. Maintain at least two valid instruments on file. This redundancy supports identity verification when primary methods encounter issues.
Concrete recommendation: Set calendar reminders for subscription renewal dates rather than relying on platform notifications. Proactive management prevents both unwanted renewals and the reactive panic that phishing exploits.
Security question answers should be random strings stored in password managers rather than discoverable personal information. Documentation of legitimate charges supports dispute resolution. Screenshot confirmations, note creator names and dates, and retain emails. This documentation proves authorized access patterns when challenging fraudulent claims.
What to Do Within the First Hour of Suspecting Breach
Response speed contains damage scope. The first hour determines whether attackers maintain access for secondary exploitation.
Immediate priority sequence:
- Change password from a clean device that was not previously used for OnlyFans access
- Check active sessions and terminate all existing logins simultaneously
- Review payment methods for unauthorized additions or changes
- Scan subscription list for unknown creators, changed prices, or unauthorized tips
- Contact support through official help center only, never through links
- Document timeline with screenshots for potential fraud claim submission
The clean device requirement prevents reinfection from potential malware. Browser-based password changes from compromised systems may capture new credentials immediately.
Session termination forces reauthentication on all devices. Combined with password change, this typically severs unauthorized connections. Payment method review includes checking for saved cards that were not personally added. The platform stores cards for tip and pay-per-view convenience. Tips can reach $100, so unauthorized tipping represents meaningful financial exposure beyond subscription costs.
Support contact through verified channels protects against ongoing social engineering. Attackers often follow credential changes with fake support outreach. Official help center submission creates ticket documentation.
Ongoing Hygiene for Long-Term Account Protection
Security maintenance prevents gradual degradation of protective measures. Quarterly reviews catch configuration drift before exploitation.
Established maintenance schedule:
- Quarterly password manager audit for duplicate or weak entries
- Biannual review of connected third-party login options and OAuth grants
- Annual verification that recovery email remains active and accessible
- Subscription inventory reconciliation against bank records
- Update of authenticator app backup codes for device replacement scenarios
Ranking site research for new subscriptions should verify creator authenticity through multiple indicators. The absence of platform discovery tools necessitates careful evaluation of external sources claiming to list top models on onlyfans.
Device hygiene extends to shared equipment. Never access OnlyFans from devices you do not control, and avoid public WiFi for account management. Cellular data or trusted VPN connections reduce interception risks.
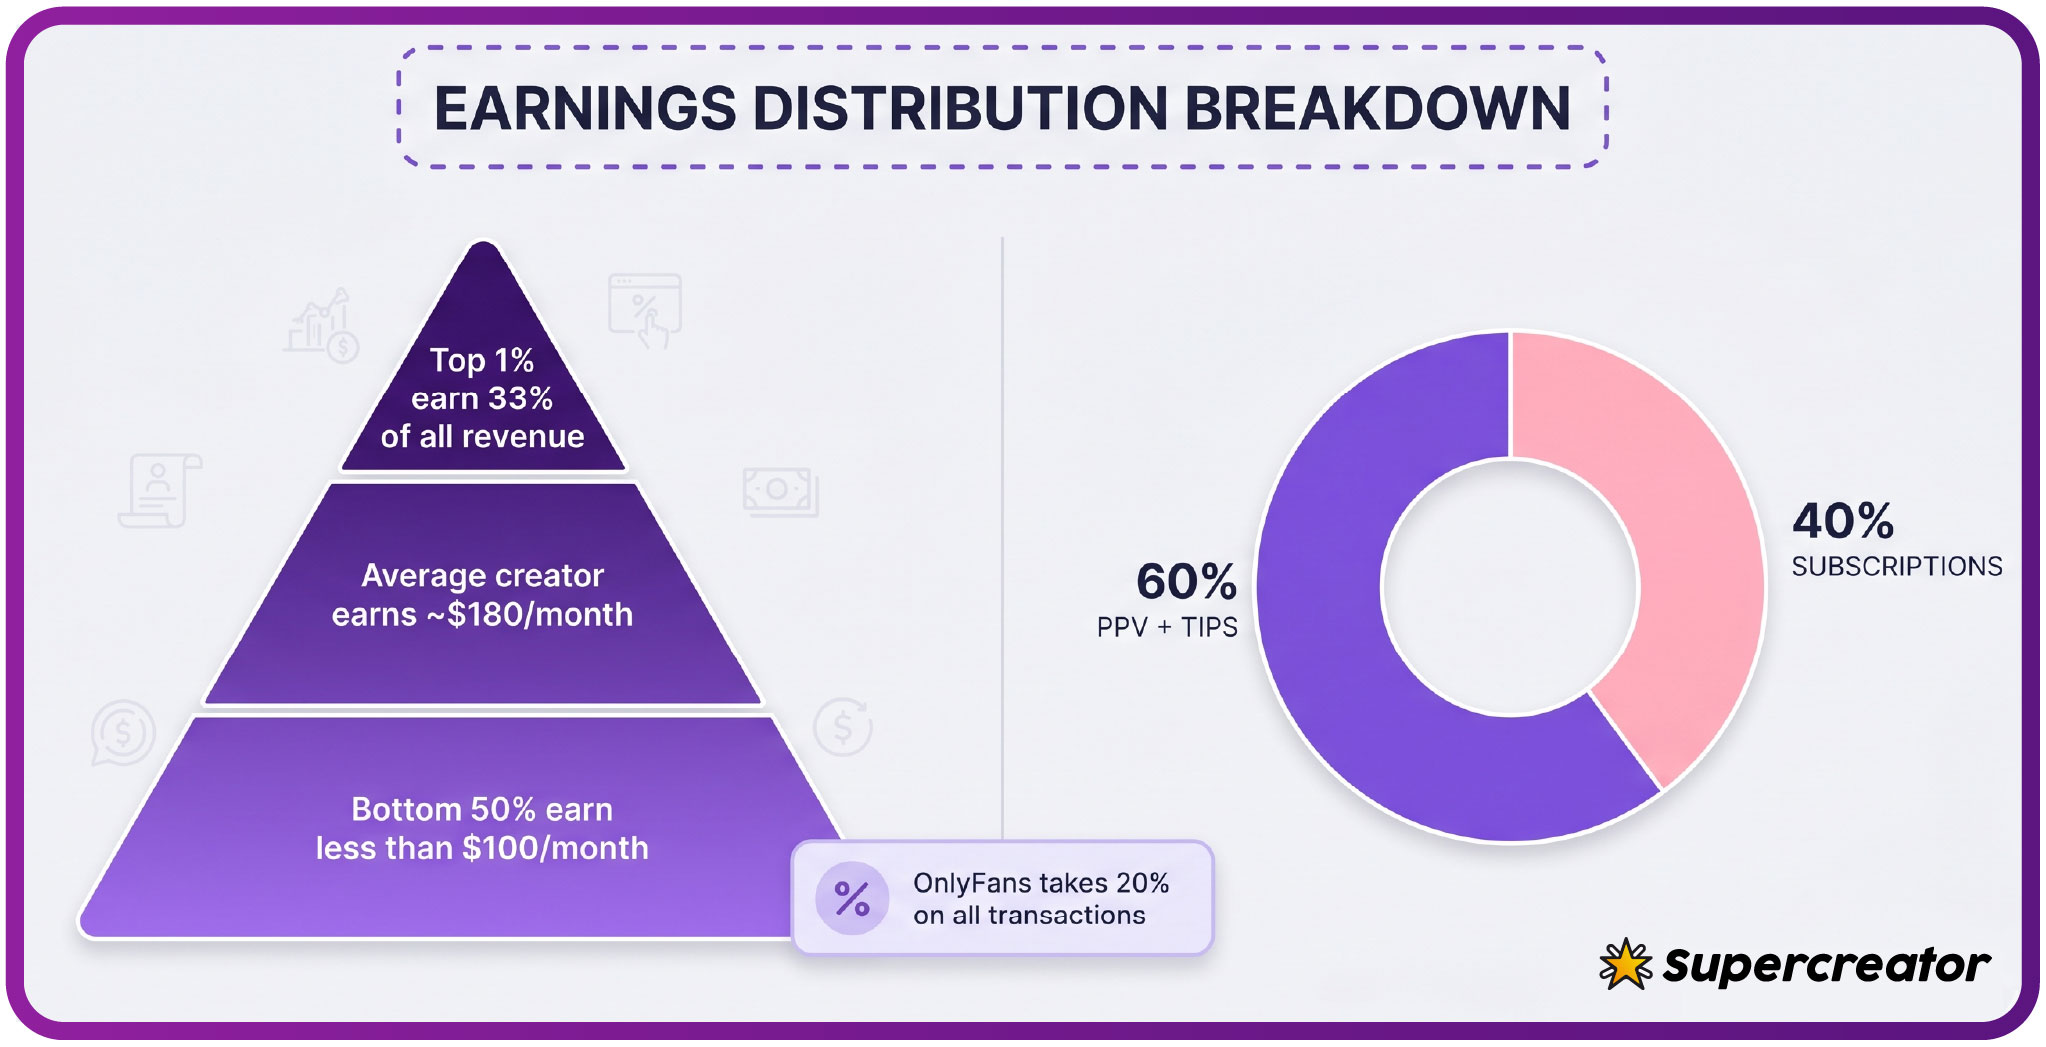
Platform fee structure explains legitimate incentive structures and helps identify fraudulent pressure for off-platform payments. The 20% platform retention and 80% creator split means legitimate creators have no reason to request external payment. Subscription audit practices include verifying that promotional pricing converted to expected base rates. Auto-renew stops when creators raise prices, but access continues until paid periods end.
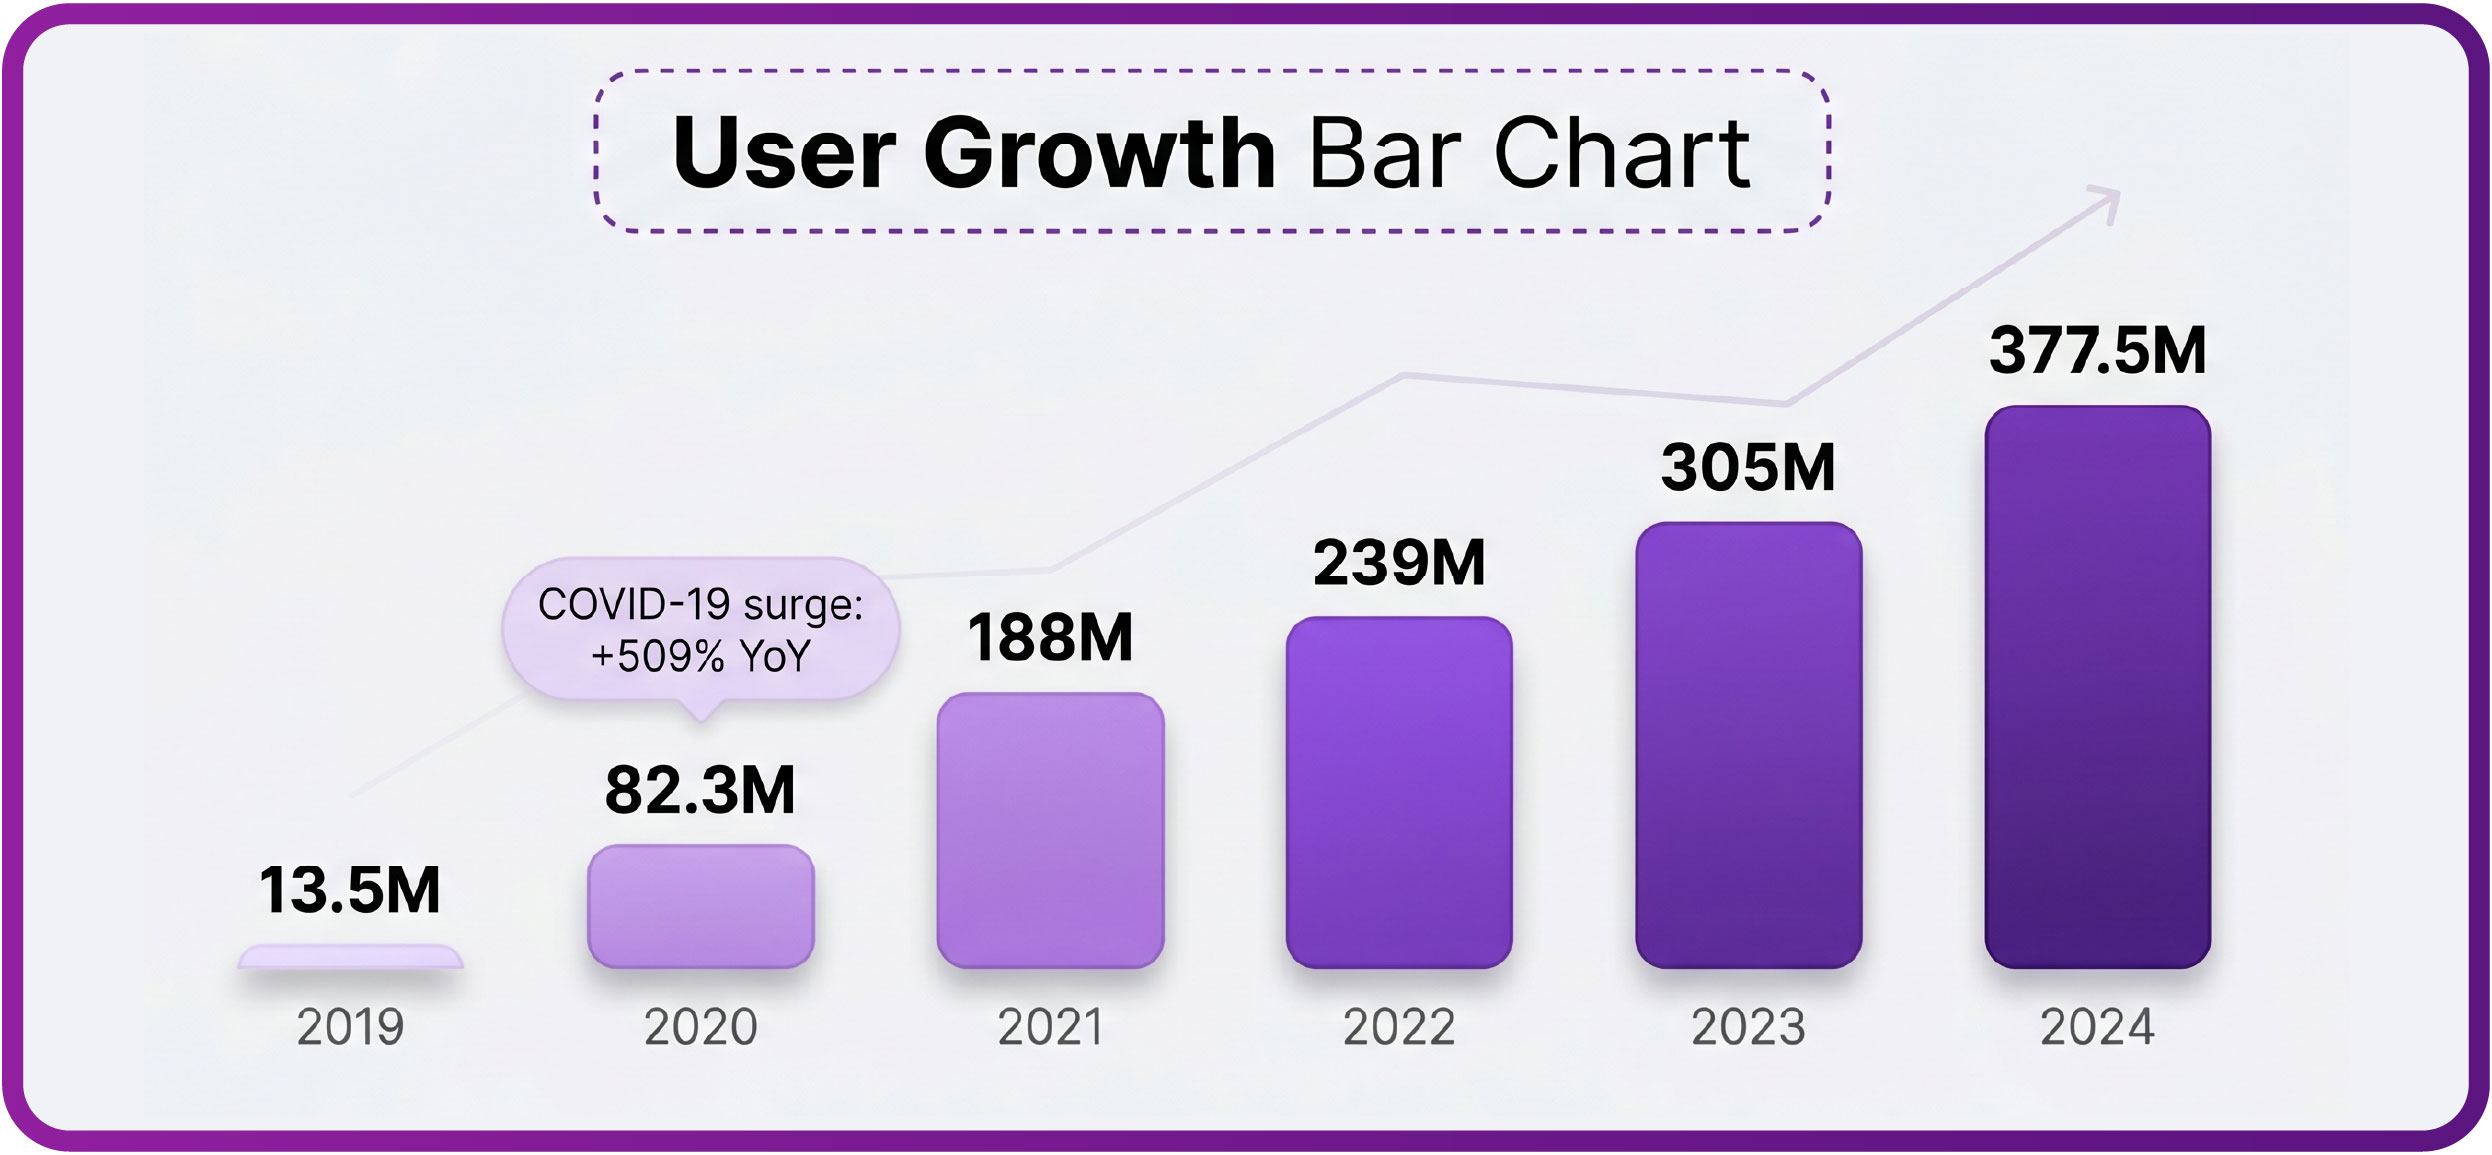
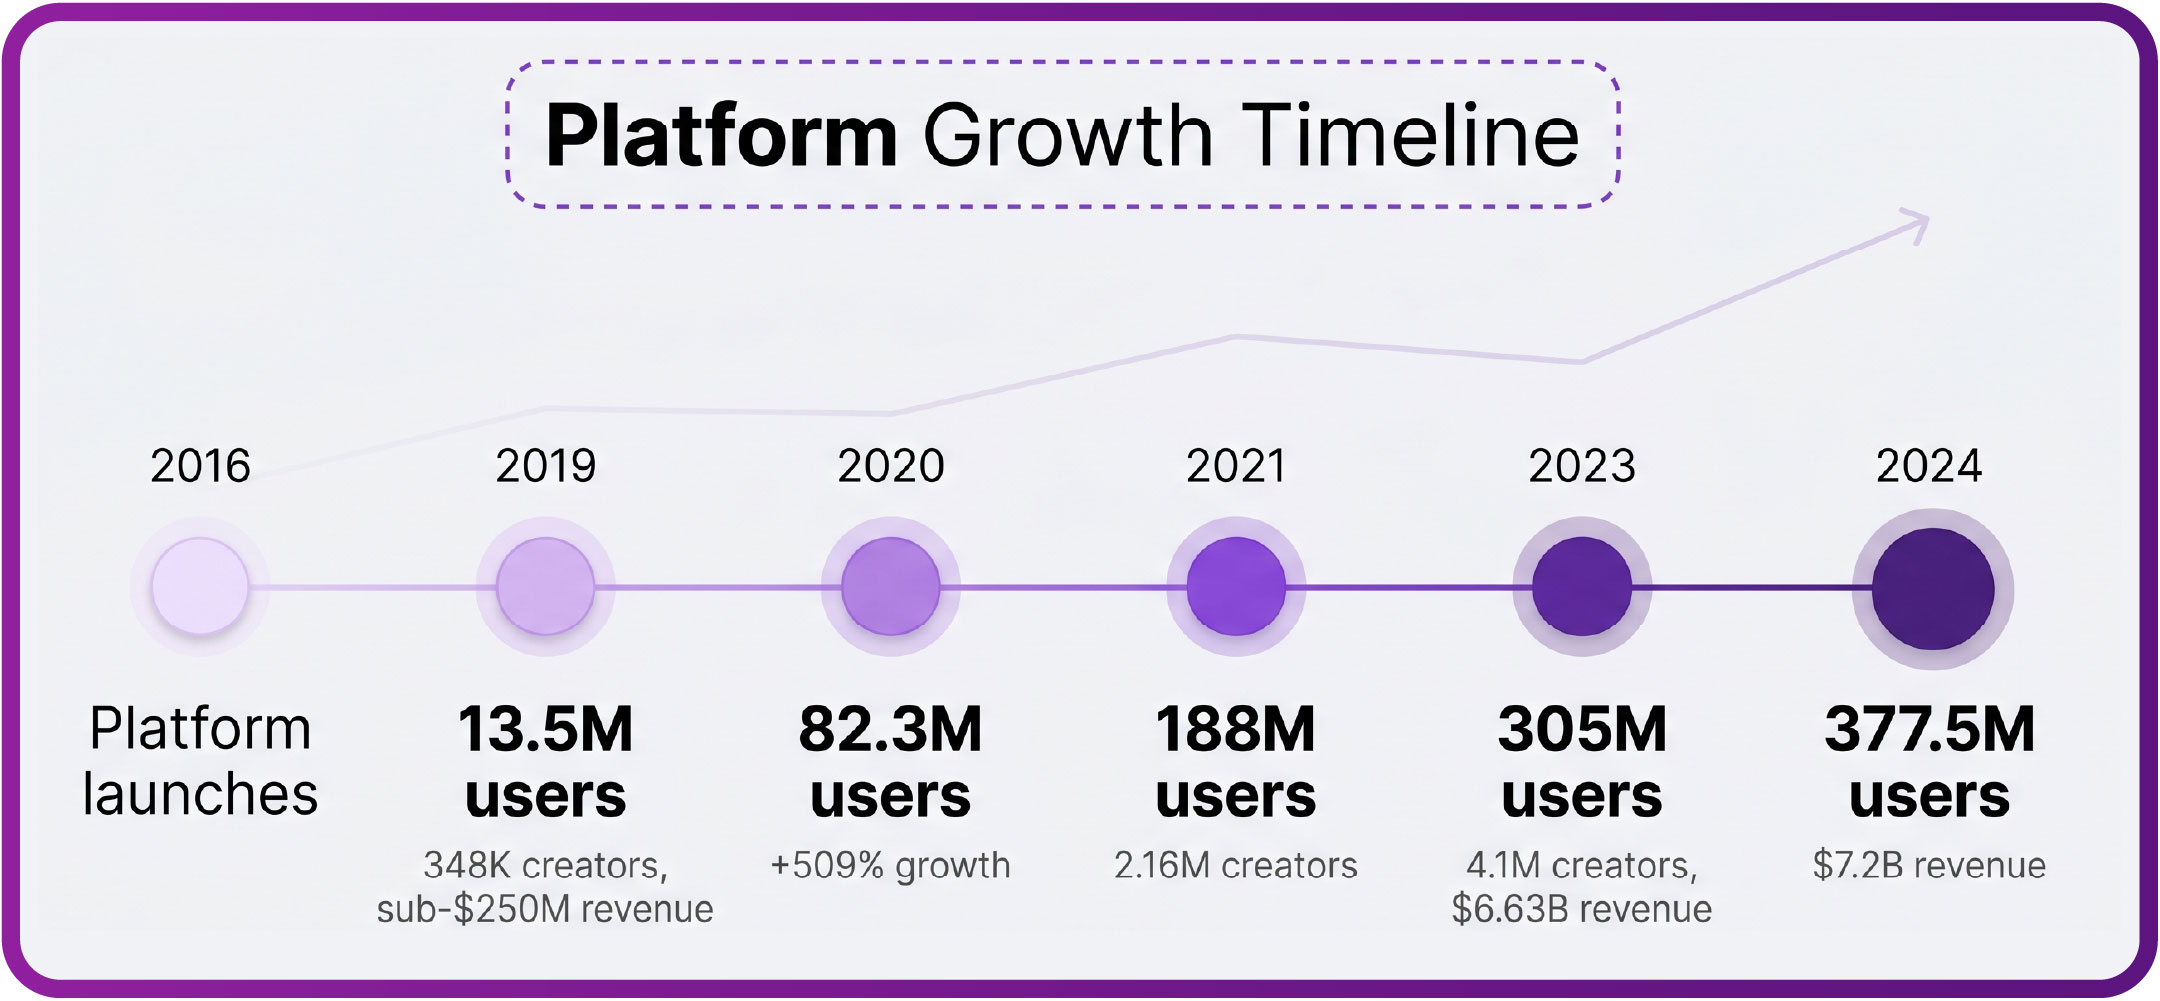
The 2020 user surge brought both increased functionality and expanded targeting. Current security posture reflects lessons from that growth period.
FAQ
Does OnlyFans ever ask for my password through email to verify my account?
No. OnlyFans never requests password entry through email links. Any message claiming account verification requiring credential re-entry is fraudulent. Access the platform directly through onlyfans.com to check account status.
What should I do if I see an OnlyFans charge I don’t recognize but my login works normally?
Unrecognized charges despite normal login suggest payment method compromise rather than account takeover. Immediately remove the payment method from your account, contact your card issuer to dispute the transaction, and review active subscriptions for unauthorized additions that might indicate credential sharing.
Are authenticator apps more secure than text messages for OnlyFans two-factor authentication?
Yes. Authenticator apps eliminate SIM swap attacks that intercept SMS codes. The platform supports standard TOTP applications. Configure backup codes during initial setup to prevent lockout when replacing devices.
Can I see all devices currently logged into my OnlyFans account?
Yes. Account settings include active sessions showing device types, approximate locations, and access times. Review this list quarterly and terminate unrecognized sessions immediately. Termination forces reauthentication on all devices.